Software für das Unternehmensrisikomanagement
Mitratech Alyne
Agile, automatisierte GRC-Technologielösungen für ein rund um die Uhr verfügbares, integriertes Risikomanagement.
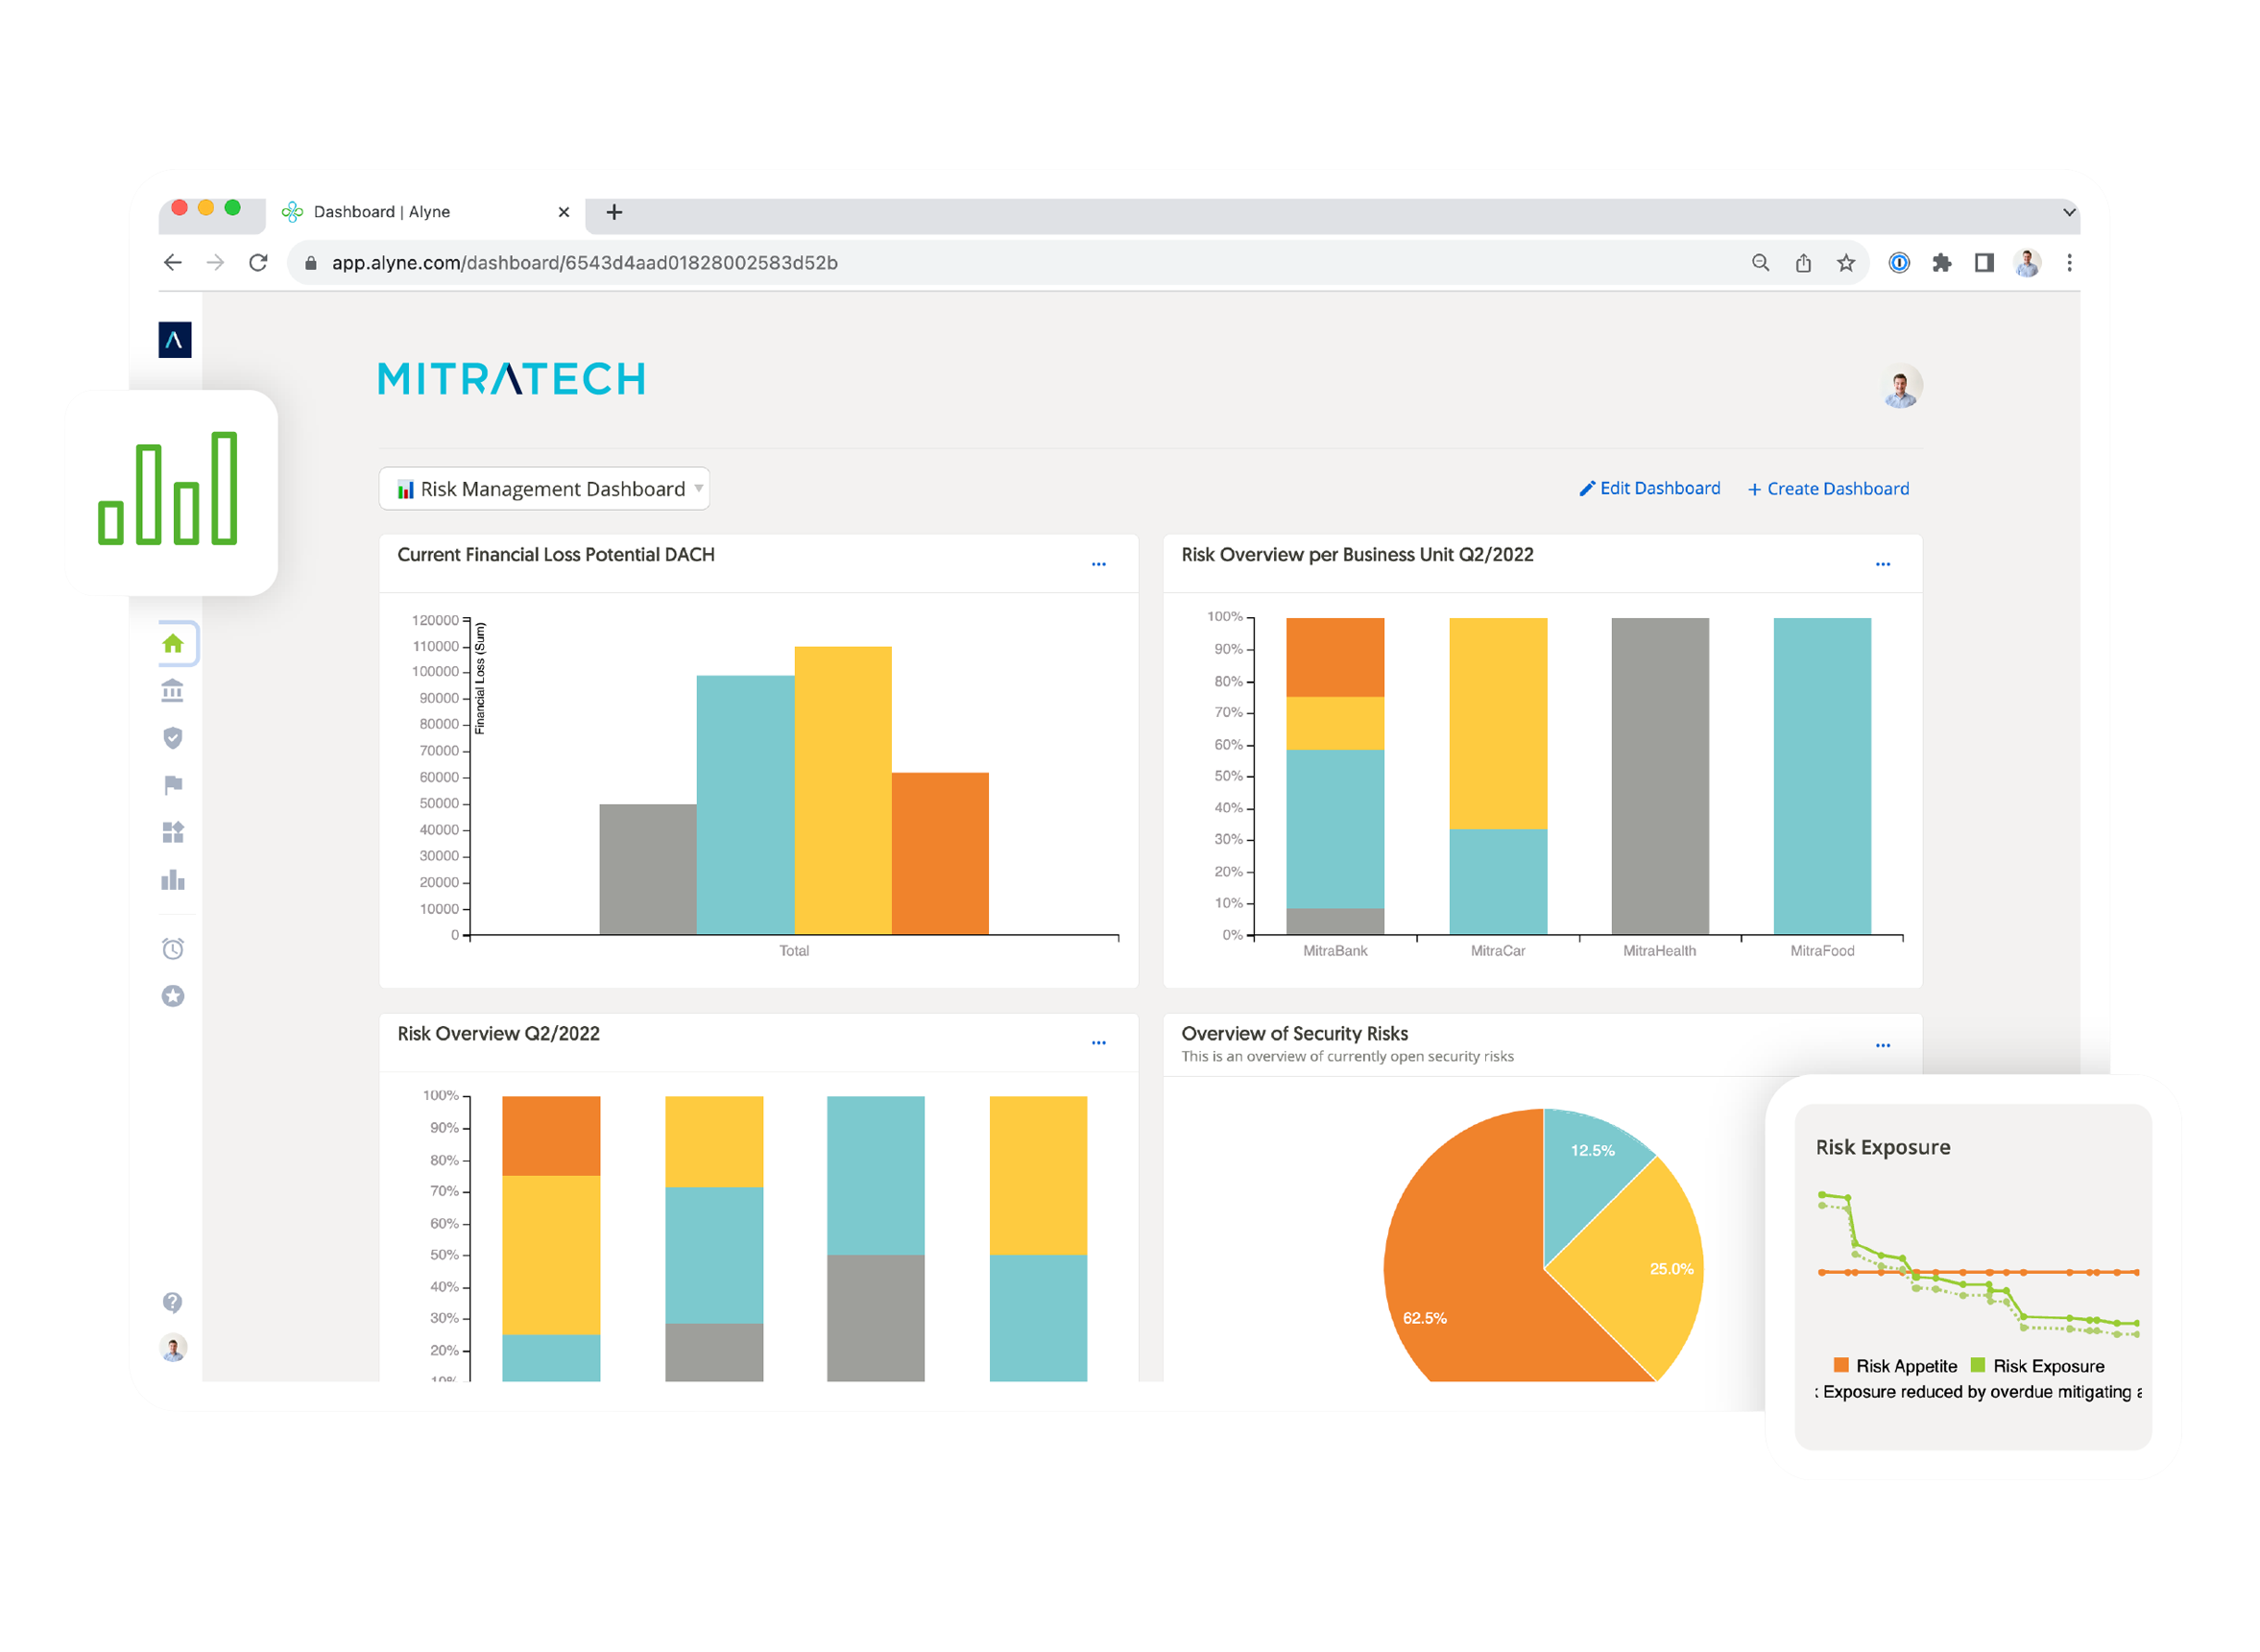
Das Risiko schläft nie.
Mitratech Alyne’s cloud-based, AI-driven governance, risk and compliance (GRC) software makes continuous risk monitoring and management easy.
From enterprise and third-party risk management to ESG and information governance, Alyne helps CISOs and risk professionals understand and assess risk, confidently implement compliance requirements, leverage and report on analytics for more risk-aware decisions, and drive 24/7, agile defense against threats.
Sichern Sie sich mit automatisierten GRC-Lösungen rund um die Uhr einen umfassenden Überblick.
Mit Alyne lässt sich Ihr Programm schnell und einfach in Betrieb nehmen – dank Workflows, die sich im Handumdrehen einrichten lassen (ganz ohne Programmieraufwand), und konfigurierbaren Dashboard-Funktionen, die die interne Zusammenarbeit fördern. Gleichzeitig arbeitet hinter den Kulissen rund um die Uhr eine leistungsstarke KI-Engine, um:
- Rationalisierung der Prozesse zur Risikoidentifizierung und -qualifizierung
- Automatisches Interpretieren von Richtlinien und operativen Dokumenten
- Quantifizierung von Risiken über eine integrierte Simulationsmaschine
- Kontinuierliche Weiterentwicklung zur Erfüllung Ihrer Anforderungen an die Einhaltung gesetzlicher Vorschriften durch neue Funktionen wie erweiterte Dokumentenzuordnung, Zusammenfassungsfunktionen und mehr
Das Ergebnis ist eine 360-Grad-Ansicht des Risiko- und Compliance-Profils Ihres Unternehmens in Echtzeit, zusammen mit Analysen, die Ihnen helfen, weiterhin die richtigen Entscheidungen zu treffen.

Sind Sie bereit, Ihre Risikomanagementstrategie zu automatisieren und jede rote Flagge zu erkennen?
ARIES™ AI for Alyne
Alyne is a SaaS RegTech platform for managing cybersecurity, governance, risk, and compliance processes. It maps regulations, frameworks, and evidence to your controls, tracks risk and mitigation in one place, and uses ARIES™ AI, with human approval, to help teams assess and respond faster.
Read and Understand, Immediately
- Document Summarization: Summarizes any regulation, standard, or policy the moment you upload it. Your team spends less time reading, more time acting.
- Evidence Summarization: Condenses supporting attachments into a quick-read summary. Reviewers can assess the evidence without opening every file.
- Document Importer: Pulls content straight out of uploaded documents into Alyne’s reader. No manual re-entry.
- Translations: Reads and writes in your team’s languages automatically. A multinational program runs in one system instead of five.
Map Controls and Catch Risk Before It Duplicates
- Automated Control Mapping: Reads a regulation or standard, finds where it overlaps your existing controls, and builds the mapping.
- Control Suggestions: Matches new requirements to controls you already have. Nobody has to search for them by hand.
- Risk Duplication Detection: Flags a new risk that looks like one you’ve already logged, before it becomes a repeat entry in the register.
- Mitigation Plan Suggestions: Suggests a mitigation plan based on the risk you just logged. Your team edits a draft instead of starting from nothing.
Agentic Risk and Compliance Action (Human-Approved, Every Time)
- Risk Agent: Works your risk and mitigation data directly, drafting mitigation plans, updating records, and generating reports. Everything lands as a draft first: risks and mitigations stay editable, reports can be reviewed and deleted if they’re off, and every referenced item links back to its page in Alyne for you to check.
- Compliance Agent: Assesses your compliance stance across questionnaires and controls, then acts on what it finds, with your sign-off required before anything changes. New controls or questionnaires are created as drafts. Never live.
- Human-approved, every time: Both agents run on the same platform authentication and product APIs you already use. Neither can access data or take an action you couldn’t already take yourself in Alyne, and any action that would change data waits for your approval before it executes.
Move Questionnaires Faster
- Automated Questionnaire Answering: Drafts answers to incoming questionnaires from the documents you already have. Your team edits instead of starting from zero.
- Automated Questionnaire Mapping: Matches supporting documents to the right questionnaire sections on its own.
- Questionnaire Review: Reviews a completed questionnaire and flags what needs a second look before it goes out.
See the Risk Picture
- Smart Widgets: Turns raw review data and team discussion into analysis you can drop straight into a report.
- Audit Question Generation: Generates audit questions and answer options directly from your control statements. Audit prep gets shorter.
- Advanced Outcomes: Writes the JSONata expression from a plain-language description. Building advanced workflow logic no longer needs an engineer.
- Integration Field Mapping: Maps your source data to Alyne’s fields automatically when you connect a new integration. No manual field-by-field setup.
Search and Draft Inside Alyne
- Global Hybrid Search: Searches across Alyne by meaning, not just keyword, and still finds the right record when you don’t remember the exact wording.
- Writing Tools: Built-in AI writing help wherever you’re drafting in Alyne.
What You Get With Mitratech Alyne
A capability-by-capability look at Mitratech’s AI-powered ERM product against a typical ERM platform, or building it yourself with AI, spreadsheets, and email.
|
MItratech Alyne |
What to ask any ERM vendor |
Built yourself with AI |
Spreadsheets and email |
|
|---|---|---|---|---|
|
Enterprise, IT, and cyber risk on a single risk foundation |
Ja |
Is it one risk foundation, or separate modules bundled together? |
Buildable. Domains stay consistent only with ongoing integration work. |
Separate files per domain, with no shared foundation. |
|
1,500+ pre-built framework and template mappings |
Ja |
How many mappings ship in the base product, which cost extra, and which named frameworks have gaps? |
Possible. Someone must write and maintain the content. |
You can reuse past files. There’s no standard library. |
|
One risk register instead of scattered files |
Ja |
Do risks across enterprise, IT, and cyber domains live in one register? |
Achievable as an internal app; only as reliable as the team maintaining it. |
Works at small scale, until versions multiply. |
|
No-code workflow configuration |
Ja |
Can your team change a workflow by configuration, or does it take a developer or vendor services? |
Buildable. Every process change becomes a development ticket. |
Manual hand-offs between steps. |
|
24/7 continuous risk monitoring |
Ja |
What does monitoring cover, and what is included versus an add-on, integration, or limited version? |
Possible with data feeds and engineering time. |
Periodic manual checks. |
|
AI-assisted control and regulatory mapping, human-approval gated |
Ja |
Is there a documented human-approval gate before AI-suggested mappings take effect? |
Possible. The approval gate must be designed and enforced by your team. |
Mapped by hand. |
|
AI governance / third-party AI risk module |
Ja |
Is it a native module or an add-on, and what does it cover? |
Possible. Someone builds and maintains the content. |
Tracked by hand. |
|
ISO 27001, SOC 2, COBIT, NIST, SOX framework-mapped reporting |
Ja |
Which frameworks are built in, and who updates them when they change? |
Mappable once. Someone must track every framework revision. |
Mapped and updated by hand. |
|
Named, shipping AI agent(s) with human-approved agentic action |
Ja |
Is the agent generally available, is there outside benchmarking, and does it have an approval gate? |
Possible. You build, test, and govern the agent yourself. |
No automation. Every step is manual. |
Governance, Risk, and Compliance Technology Leader
Um den Risiken der heutigen Zeit zu begegnen, ist modernste GRC-Software erforderlich
-

Identifizierung von Compliance- und Regulierungsanforderungen
Abdeckung der Vorschriften: ISO 27001, SOC 2, SS1/22 & SS2/22, COBIT, NIST, CCAR, sr 11-7, DFAST, SOX, TRIM & mehr.
-
Intuitive UI und UX
Verbessert die Akzeptanz und die Zusammenarbeit im gesamten Unternehmen und erfordert keine Schulung für die Nutzung.
-
Integrationen in Echtzeit
Integrationen mit Drittanbietern von Daten. Darüber hinaus können Sie mit PlatoBI DataShare for Alyne Ihr eigenes Snowflake- oder Business Intelligence (BI)-Tool über Snowflake mit Ihren Alyne-Daten verbinden und erhalten so einen ganzheitlichen Überblick über die Risiken Ihres gesamten Techstacks, unabhängig davon, ob die Quellen Teil der Mitratech-Suite sind.
-
KI- und ML-Engine
Alyne verbindet von Experten geschulte künstliche Intelligenz mit maschinellem Lernen, um den Nutzern zu helfen, Vorschriften zu erkennen und zu verstehen und dann die Risiken zu mindern und darüber zu berichten.
-
Code-freie Arbeitsabläufe
Senken Sie die Betriebskosten durch eine codefreie Konfiguration und Arbeitsabläufe, die es auch technisch nicht versierten Benutzern ermöglichen, Alyne an ihre Bedürfnisse anzupassen.
-
1.500 sofort einsatzbereite Vorlagen
Minimieren Sie Risiken in einem Bruchteil der Zeit, indem Sie über 1.500 vordefinierte Vorlagen nutzen, die den Vorschriften und Kontrollen zugeordnet sind.
Ein Partner. Eine Plattform.
Alles, was Sie benötigen, um Ihr Governance-, Risiko- und Compliance-Programm zu vereinheitlichen.
Erfahren Sie, wie Alyne die Einhaltung von Vorschriften beschleunigt
"Wir sind begeistert, dass wir bereits sechs Wochen nach der Implementierung in der Lage waren, unseren Risikoinventarisierungsprozess vollständig innerhalb von Alyne durchzuführen, was den internen Abstimmungs- und Koordinationsaufwand erheblich reduziert und die Transparenz und Qualität des Risikoinventars deutlich erhöht.
Integrierte GRC-Tools und Softwarelösungen für jeden Anwendungsfall
Von Enterprise Risk Management (ERM) und Datenschutz bis hin zu Policy Management und QHSE Incident Support - entdecken Sie integrierte GRC-Tools und Softwarelösungen für jeden Bedarf.
-
Lösungen für das Risikomanagement von Drittanbietern
Proaktive Überwachung und Abschwächung von operationellen Dritt-, Viert- und Drittparteirisiken, Erhöhung der Transparenz und der Fähigkeit, bei Bedarf schnell zu handeln.
-
Information Governance-Lösungen
Bessere Erfassung, Speicherung, Analyse und Verwaltung Ihrer Daten in Übereinstimmung mit den Unternehmensrichtlinien und gesetzlichen Vorschriften.
-
Lösungen für Unternehmensrisikomanagement (ERM)
Verankern Sie das Risikomanagement in Ihrem Unternehmen - und werden Sie zum strategischen Partner für alle.


Alyne Resources
Informieren Sie sich über umfassende Risikobewertungen, Berichterstattung und automatisierte GRC-Software.
Verbinden Sie Risikodaten mit Alyne für eine ganzheitliche Sicht auf Risiken in Ihrem Unternehmen
Jetzt herunterladen!Häufig gestellte Fragen
What is Mitratech Alyne?
Alyne is a cloud-based risk and compliance solution that provides continuous risk monitoring and management through automated workflows, dynamic dashboards, and real-time visibility into an organization’s risk and compliance profile. It uses AI to streamline risk identification, policy interpretation, and compliance tracking.
What are the key capabilities of Alyne?
Alyne includes dynamic dashboards and reports, scalable risk assessments, over 1,500 ready-to-use templates, no-code workflows, enterprise integrations, and agentic AI capabilities and automation for risk identification and compliance management. The platform is fully web-enabled and mobile-responsive.
How does Alyne use AI?
Alyne’s AI engine streamlines risk identification and qualification, automatically interprets policies and operational documents, quantifies risks through a built-in simulation engine, and supports advanced document mapping and summarization. Beyond analysis, the ARIES™ Risk Agent takes action on your behalf, managing the risk library, surfacing coverage gaps, and generating executive reports on demand, all within your organization’s data environment. The engine evolves continuously to keep pace with regulatory changes.
What compliance frameworks and regulations does Alyne support?
Alyne supports ISO 27001, SOC 2, SS1/22 and SS2/22, COBIT, NIST, CCAR, SR 11-7, DFAST, SOX, TRIM, and additional frameworks. Organizations can map controls to multiple frameworks simultaneously using Alyne’s template library.
What are the primary use cases for Alyne?
Alyne supports enterprise risk management (ERM), IT/Cyber risk management, AI & information governance, policy management, data privacy, ESG, and QHSE incident management.
Does Alyne require technical expertise to configure?
No. Alyne features no-code workflows and configuration that non-technical users can manage independently. The interface requires limited onboarding to navigate.
Can Alyne integrate with other systems?
Yes. Alyne offers real-time integrations with third-party data providers. PlatoBI DataShare for Alyne connects your BI tools to Alyne data via Snowflake, giving organizations a consolidated view of risk across their technology stack. Additionally, Alyne integrates with multiple products across the GRC portfolio.
Is Alyne cloud-based?
Yes. Alyne is a cloud-based platform with a fully web-enabled, mobile-responsive design. No local installation is required.
How does Alyne differ from other risk and compliance platforms?
Alyne combines over 1,500 pre-built templates, no-code configuration, and an AI engine that automatically interprets policies and quantifies risks through simulation in a single cloud platform. Alyne’s ARIES™ Risk Agent takes this further by actively managing the risk library, surfacing coverage gaps, and generating executive reports on demand, all within the customer’s own data environment. Non-technical users can configure and operate the platform without IT involvement, and the template library covers a broad range of regulatory frameworks out of the box.
What is ARIES in Alyne?
ARIES™ is the AI layer built into Alyne’s workflows. It reads incoming regulations and evidence, maps what it finds against your existing controls, and flags new risks that resemble ones you’ve already logged. It also drafts first-pass mitigation plans and audit questions, so your team edits rather than starting from a blank page.
Can ARIES change my data without approval?
No. The ARIES Risk Agent and Compliance Agent can act directly on your risk and mitigation data, but nothing changes until someone on your team approves it. Your people stay the decision-makers, and the agents do the preparation.
©2026 Mitratech, Inc. Alle Rechte vorbehalten.
©2026 Mitratech, Inc. Alle Rechte vorbehalten.